Guard rails come standard.
Every app Lucity builds from your code is checked for leaked keys on each deploy, and for known vulnerabilities for as long as it runs. Every workspace is walled off from the next. Nothing to install and nothing to configure, on every plan.
- On every plan, the trial included
- Never holds a release back
- Open source, so you can read how it works
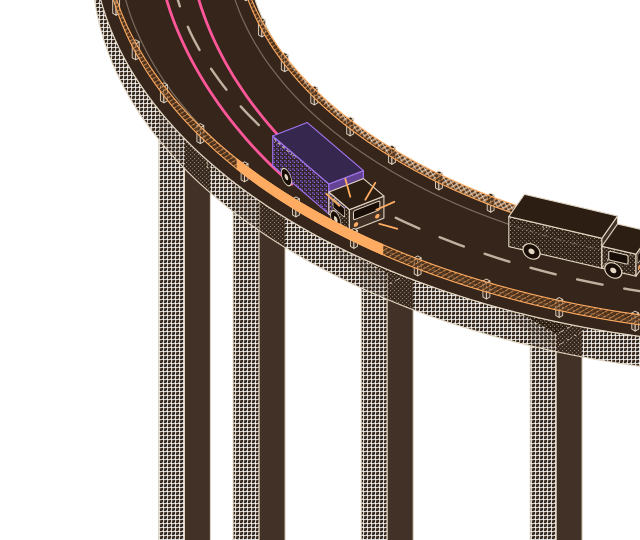
You push. The build starts, and a scan for leaked keys starts with it.
The scan finds an AWS key in your history and asks AWS whether it still works. It does.
Nothing is blocked. The release ships, and the finding waits in the Security tab.
Two hours later the running app is checked again. A vulnerability announced today shows up on what you shipped before.
Build and Secrets run side by side. The scan reports what it finds and never holds a release back.
Leaked keys ,
caught on every deploy.
Each deploy reads your repository for passwords, API keys and tokens, next to the build. What it finds lands on the Security tab of the service, with the keys that still work at the top.
Rotate first.
Deleting the file does not take a key out of your history. Rotating it is what makes it harmless, and the finding stays for as long as the commit does.
Vulnerabilities ,
checked while your app runs.
Lucity rechecks every running app it built, every two hours. A vulnerability announced tomorrow shows up on the app you deployed last month.
It keeps looking after you ship.
A check at build time goes quiet the moment the build is done. This one runs against what is live, so the list changes when the world does.
Rechecked every two hours since. No new deploy was needed for the finding to show up.
Walls ,
between everything.
Lucity runs code from many customers on shared machines, so isolation is the first design rule and not a setting you find later.
And when something goes wrong anyway: a database restores to any second of the last 30 days, a release rolls back to the one before, and a broken deploy never replaces a working one.
Agents work inside the same rails.
Let a coding agent deploy, debug and read logs for you. The Lucity tools it gets are built so that it can do the work without holding your secrets.
This covers what the Lucity tools return. An agent that reads a .env file on your laptop sees what is in it. How the plugin handles secrets
Answers for your security review.
The short version for whoever reviews your vendors. Where we do not have something yet, it says so.
Last reviewed 12 November 2026
What reviewers ask us
Still wondering about something? Ask us
No. The scan for leaked keys runs next to the build and reports what it found. The release ships either way, and a failed build never replaces the version that is already running.
Only to ask the key's own provider whether it is valid, with a read-only request. Found keys are stored masked, and only members of your workspace see the findings.
A finding belongs to a commit, so it stays while that commit is in your history. The mark that a key still works is set when the key is found and is not checked again on later deploys yet. Rotating the key is what makes it harmless.
Every app Lucity builds from your repository, in every environment. Prebuilt images from public registries are not scanned yet.
Requests reach your apps through a global edge network, and some platform logs and metadata are analyzed with an AI provider in the United States under standard contractual clauses. The data processing agreement lists every sub-processor.
Yes. Lucity is open source, so they can check how scanning and isolation work instead of taking our word for it.
Hand this page to your security team.
Send us your questionnaire and we will fill it in. Or deploy something small and open its Security tab, which is the quickest way to see all of this for yourself.